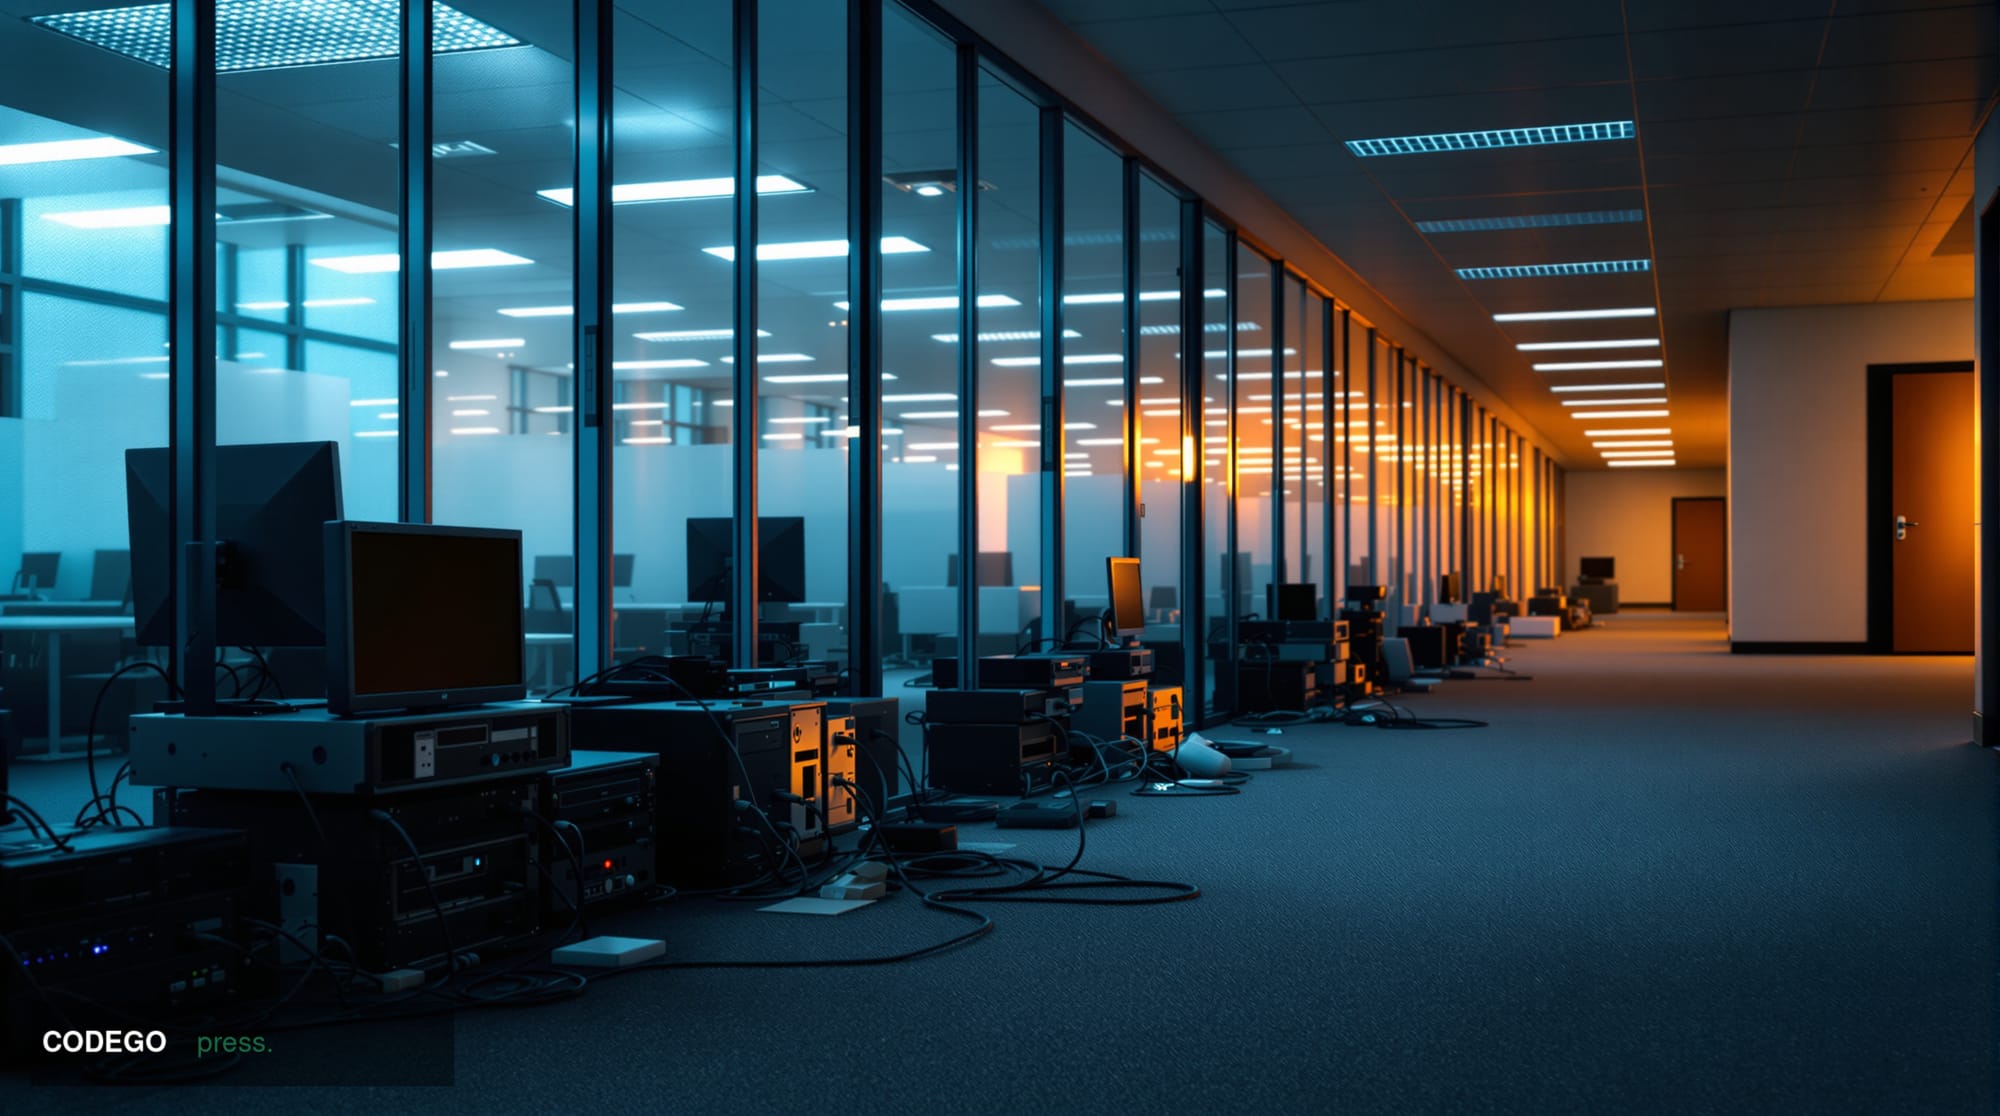
When a federal agency abandons its offices and leaves sensitive hardware behind — unattended, unsecured, and unaccounted for — the lapse is more than administrative untidiness. It is a measurable failure of institutional stewardship. That is precisely what the Consumer Financial Protection Bureau allowed to happen after vacating its regional offices in early 2025, a misstep that only came to light when a government watchdog formally flagged the risk more than a year later in a report published September 30, 2026.
The Office of Inspector General for the Board of Governors of the Federal Reserve System — the oversight body with jurisdiction over the CFPB — issued the report on that Wednesday, recommending that the bureau take immediate steps to secure hardware assets left behind at offices the agency had walked away from. In response, the CFPB moved to clear the equipment from those vacated premises. The corrective action, while necessary, arrived only after external pressure, raising pointed questions about the bureau's internal asset-management protocols during a period of significant institutional turbulence.
An Agency in Contraction
The backdrop to this episode is impossible to ignore. The CFPB's closure of regional offices in early 2025 was part of a broader contraction of the bureau under political and budgetary pressures that reshaped its operational footprint dramatically. Regional presences were wound down, staff reductions followed, and the agency's enforcement posture became considerably more restrained. Against that context, the failure to properly inventory and secure physical hardware assets is less surprising — but no less troubling. Rapid organizational downsizing, if not managed with rigorous discipline, creates exactly the kind of asset-custody gaps that adversaries — domestic or foreign — are positioned to exploit.
Hardware left in vacated federal offices is not simply a matter of misplaced government property. Depending on what data those devices contain, or what network credentials remain stored on them, the security implications can extend well beyond the CFPB itself. Financial supervisory bodies handle sensitive data relating to consumers, regulated institutions, and ongoing enforcement matters. Any device carrying fragments of that information, left in an insufficiently controlled environment, represents a potential vector for unauthorized access, data exfiltration, or worse.
The Watchdog's Role and Its Limits
The OIG's intervention here reflects exactly the kind of oversight function that Inspector General offices are designed to perform — identifying institutional failures that internal management has missed or deprioritized. That the OIG needed to step in at all, however, underscores a structural concern: the CFPB's own internal controls were insufficient to catch and remedy this lapse without external prompting. Standard asset-management practice for any federal agency — let alone one handling sensitive financial regulatory data — requires a documented chain of custody for hardware at every stage of an office lifecycle, including decommissioning and relocation.
The fact that this hardware remained unsecured for a period that apparently stretched well past the early-2025 office closures before the September 2026 OIG report brought it to light suggests that the bureau's asset-tracking discipline was not operating at the standard expected of a financial regulatory body. Whether the hardware has since been forensically examined for any signs of unauthorized access or data compromise is not addressed in the available reporting — and that omission itself is a data point regulators and oversight committees may wish to press.
Institutional Trust Is Hard to Rebuild
For a bureau whose central mandate is protecting consumers from financial harm, the reputational dimension of this episode carries particular weight. The CFPB has spent much of the last decade defending both its constitutional legitimacy and its operational credibility against sustained political and legal challenge. Episodes that suggest internal management dysfunction — even ones eventually corrected — hand critics a ready argument that the agency lacks the organizational discipline required to execute its mandate effectively.
The bureau's decision to act on the OIG's recommendation and clear the hardware from vacated offices is the right outcome. But it is a reactive outcome, not a proactive one. Responsible asset governance in a federal regulatory environment demands that decommissioning plans be in place before offices are vacated, not assembled in response to a watchdog's formal written warning issued more than a year after the fact. The CFPB, if it is to restore the institutional confidence it needs to function credibly, must demonstrate that this episode has prompted a genuine audit of its asset-management procedures rather than a targeted fix applied only to the specific offices the OIG identified.
What This Means for Financial Oversight
This episode carries lessons beyond the CFPB alone. Across the federal financial regulatory landscape, agencies that have undergone rapid workforce reductions, office closures, or structural reorganization face analogous risks of asset-custody breakdowns. The OIG's intervention serves as a timely reminder that hardware security is not a peripheral IT concern — it is a core component of any institution's data-security posture and, by extension, its regulatory integrity. Oversight bodies, congressional committees, and agency leadership alike should treat this case as a prompt to audit their own decommissioning protocols, before a watchdog report makes the audit unavoidable.
Written by the editorial team — independent journalism powered by Codego Press.